
Securing Software Delivery Pipelines in the Age of AI: Introducing OWASP SPVS
First look at SPVS 2.0.
It ships Friday, and Farshad and Cameron announce it live in this talk. The slides go up the same day.
Your pipeline has access to your source, your secrets and production, and attackers know it: Cameron counted 75 public pipeline incidents from January to July 2026. SPVS is the OWASP standard for assessing your pipeline across five stages, at three levels, including controls for AI agents.
- 1.
Why the delivery pipeline is now one of the most attacked parts of the software ecosystem, from source control to runtime, including AI-assisted and agentic tooling.
- 2.
How SPVS assesses a pipeline across Plan, Develop, Integrate, Release and Operate, at three levels.
- 3.
How to use SPVS as a roadmap: start at Level 1, close the gaps that matter, and keep it current.
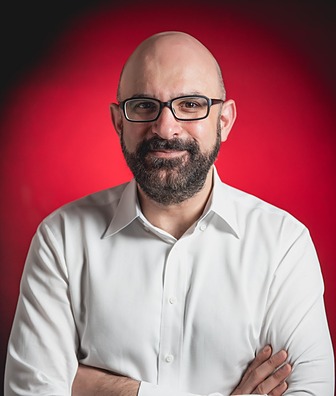
Founder and CEO, Forward Security · Co-founder and Co-CEO, Eureka DevSecOps
More than 20 years in security, software design and system architecture, including a decade on HSBC's IT security team. Leads the OWASP Vancouver chapter and co-leads OWASP SPVS. CISSP.
Connect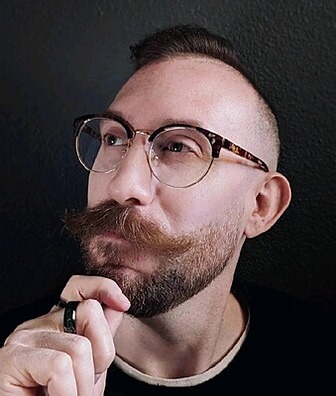
Director, AppSec and Security Engineering · Co-lead, OWASP SPVS
Co-host of Coffee & Chaos and the ProdSec Podcast, and leader of CYBERLUNCH, the Austin security meetup.
Connect