
Don't let AppSec be the reason your growth stalls.
Eureka scans your code, finds which vulnerabilities an attacker could chain together, and tells you the few to fix first. Press Autofix and it writes the fix and opens a pull request. You review and merge.
30-day free trial. No credit card required.
From scan to merged fix.
Eureka scans your code
Eureka Managed Scans runs SAST, SCA and secrets scanning on your repositories and collects every finding.
Eureka finds the attack scenarios
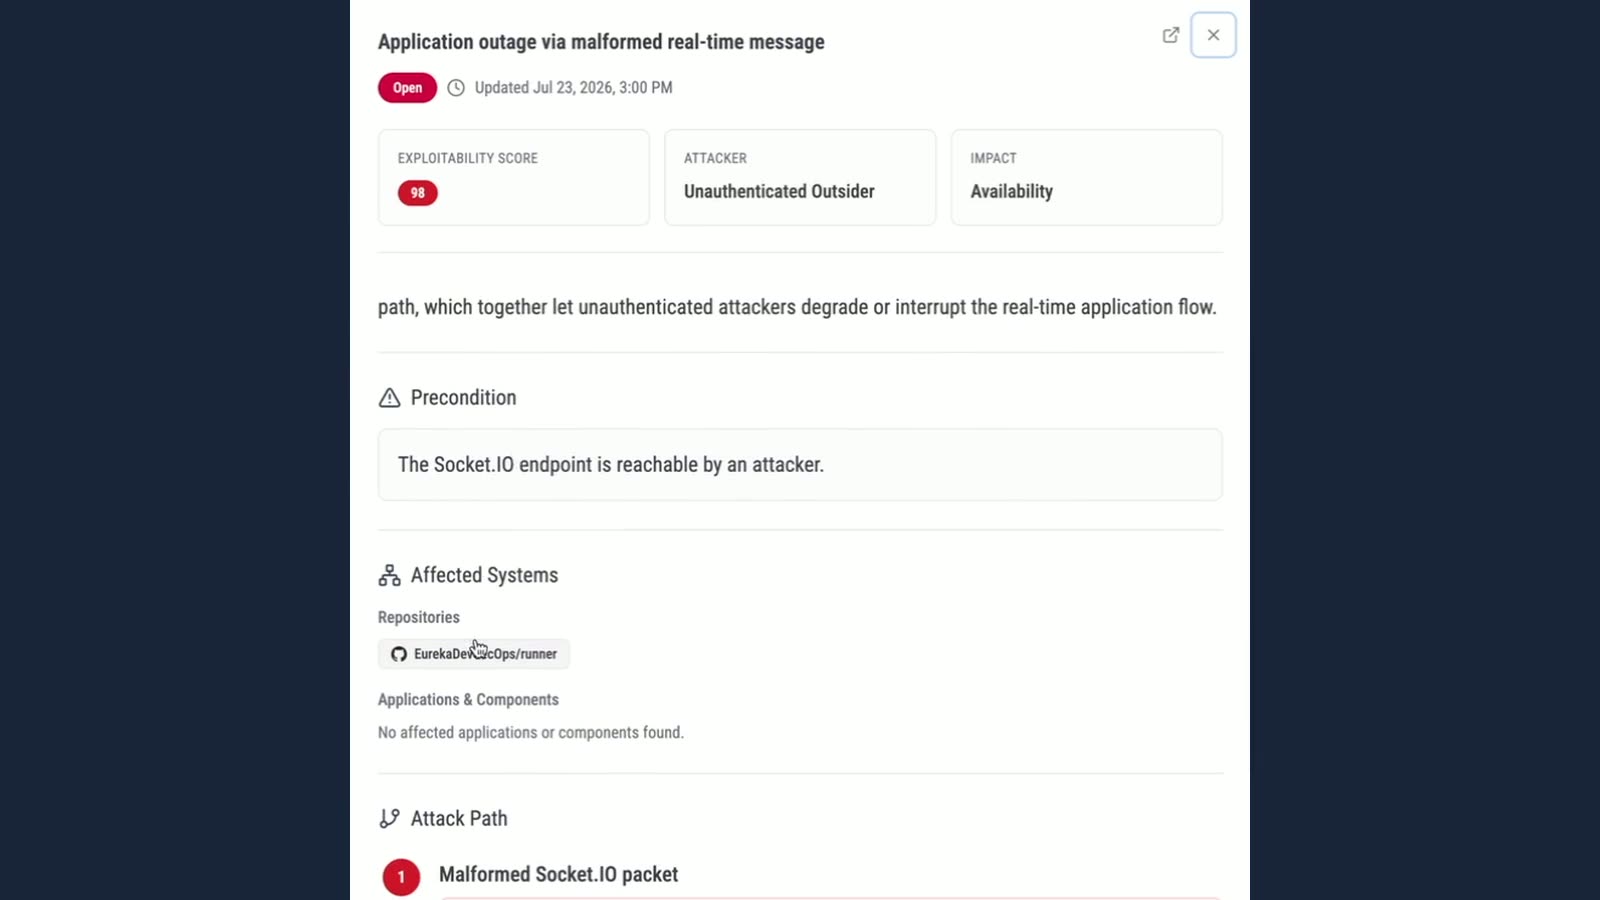
Eureka threat-models your application and chains vulnerabilities into attack scenarios.
Eureka ranks what to fix first
Every attack scenario gets a score. The higher it is, the more likely it can be exploited. Fix those first.
Eureka writes the fix
Click Autofix on a finding in a GitHub repository. The agent writes the fix, scans again to check the vulnerability is gone, and opens a pull request.
You review and merge
Review the pull request and merge it. Eureka keeps the audit history: what was found, what changed and who approved it.
AI makes it easier to find the weaknesses attackers can use.
Turn AI-era discovery pressure into attack-scenario priority, remediation workflow and evidence captured as work happens.
AI turns discovery pressure into a clear remediation order.
Trusted by software, security and regulated teams
Built by leaders behind two OWASP standards: ASVS and SPVS.


Security should not block your growth
Eureka helps your team start from the right AppSec workflow and build a connected AppSec record of what was found, assessed, fixed and approved.
- Launch a new AppSec program.
- Prioritize growing scanner backlogs.
- Prepare for customer assurance.
- Support an upcoming submission.
Is AppSec starting to stall growth?
Start application security with built-in code, dependencies, secrets and supply-chain checks, plus prioritization and audit history without scanner wrangling.
Too many findings, no clear priority?
Eureka helps your team use attack scenarios, AppSec context and decision history to focus on the 1% of vulnerabilities that matter, not every scanner finding.
SOC 2 or customer review coming up?
Show how AppSec findings were tested, reviewed, fixed and approved before SOC 2, enterprise review or customer due diligence turns into a scramble.
Submission coming up?
Build cybersecurity documentation directly from real AppSec activity across scans, fixes, releases and decisions without rebuilding the evidence trail during submission week.
From scanner output to what actually matters
Eureka reduces hundreds of raw findings to the small set of vulnerabilities your team should fix first.
Vulnerability status your team can actually read.
One view of what was found, what is being fixed and what has been resolved, the same record customer assurance, audits and submissions draw from.

Real teams use Eureka to make AppSec easier to run
A snapshot of how a customer team runs day-to-day AppSec with Eureka, findings, fixes and evidence captured as work happens.

“It just makes everything so much easier, especially for a team like ours. We’re a smaller team of about ten developers, and until recently we didn’t have someone dedicated to security. Having Eureka, where we can one-button-click turn it on, is awesome.”
Frequently asked questions.
Eureka is built for software teams that need application security to be easier to run, easier to prioritize and easier to prove. Here are the questions that usually come up first.
Eureka is an AppSec workflow platform. It can run built-in checks or bring in supported scanner output, then connect findings to prioritization, remediation, decisions, and evidence captured as work happens.
Eureka is built for software teams that need stronger AppSec without building a large security program first. That includes B2B SaaS teams selling to enterprise customers, teams preparing for customer reviews or SOC 2, regulated software teams, and engineering teams managing too many scanner findings.
Yes. Eureka helps teams show what was scanned, what was found, what was reviewed, what was fixed or accepted, who made each decision, and what evidence was captured. It does not replace an auditor or GRC platform.
Usually not. Scanners find issues. GRC platforms manage broader compliance programs. Eureka connects AppSec findings, prioritization, remediation, decisions, and evidence into one workflow.
Teams can begin by connecting a repository and running a first scan. Eureka supports built-in checks, managed scanning, Radar CLI workflows, and supported scanner imports so teams can start without first building a complex scanner stack.
More scanners create more findings. Eureka helps teams decide what matters, assign ownership, track remediation, document decisions, and keep the AppSec record connected over time.
Know where you stand.
No scanner wrangling. No spreadsheet evidence scramble. No rebuilding the trail during review week.
Findings, fixes, decisions and audit history stay connected as work happens, so customer reviews, audits and submissions all draw from the same record.